3 posts

social engineering

Diagram of an adversary-in-the-middle phishing attack: a user enters credentials on a fake website, which passes them to the attacker, who uses them on the real website

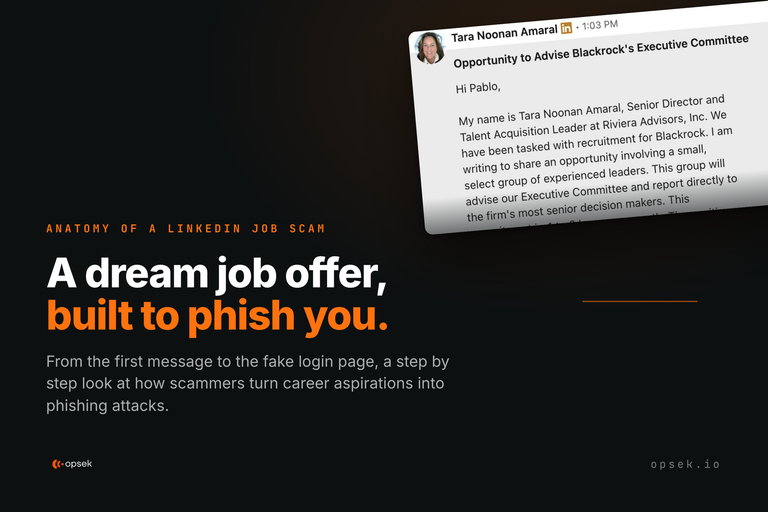
Anatomy of a LinkedIn Job Scam

Carlos Finos ―

From the first message to the fake login page, a step by step look at how scammers turn career aspirations into phishing attacks. An InMail offering a BlackRock advisory seat. An InMail arrived on LinkedIn at 1:03 PM offering a Strategic Advisor seat on BlackRock’s Executive Committee. Four to six hours a month. An annual retainer between $190,000 and $275,000. The sender introduced herself as a
News opsec Scam rekt social engineering 1password
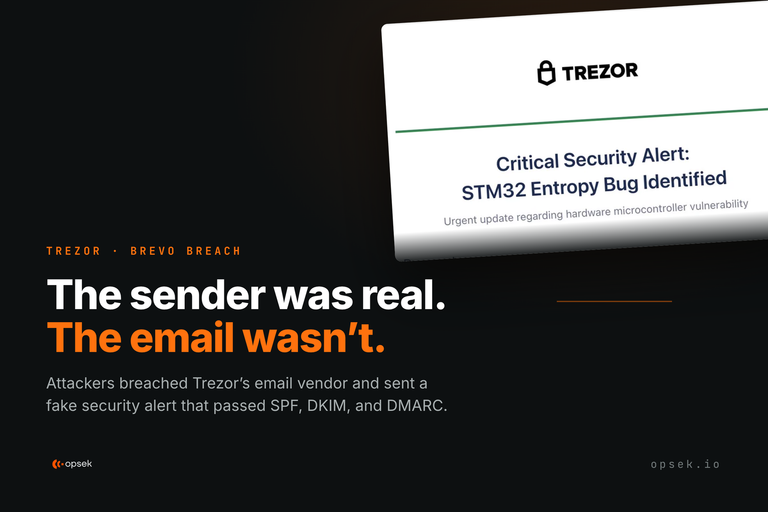
Trezor Brevo breach blog cover — fake 'Critical Security Alert: STM32 Entropy Bug' phishing email that passed SPF, DKIM, and DMARC

Trezor: 347,000 Users Phished After Attackers Breached Its Email Provider.

Carlos Finos ―

On September 9th, attackers compromised Brevo (the email platform behind Trezor's newsletter) and sent a fake security alert to roughly 347,000 subscribers. Trezor wasn't the only one hit: BitBox and CoinTracking got caught in the same net. The email looked legitimate to subscribers. It came from the official help@trezor.io address, with headers referring to mailing.trezor.io, and it passed standard SPF, DKIM,

News opsec password manager rekt Scam social engineering 1password infostealers
THE OPSEC WAKEUP CALL

THE OPSEC WAKEUP CALL

Pablo Sabbatella ―

A recap and takeaways of some stuff we talked about some days ago during the "Don't Get Rekt" episode 4 "THE OPSEC WAKEUP CALL" by RektHQ with @officer_secret: DPRK, Operational security, physical security and kidnappings, Bybit, hardware wallets, and more. Current status of web3 security: 99% of stolen funds are not due to smart contract hacks anymore, but Operational security issues, this means

rekt opsec dprk north korea lazarus social engineering password manager

Stay in the loop

Subscribe to get the latest updates, straight to your inbox.