5 posts

password manager

The Ledger CryptoBilis supply-chain attack: what the hidden implant means for your seed phrase.

The Ledger CryptoBilis supply-chain attack: what the hidden implant means for your seed phrase.

Louis Marquenet ―

At 04:59 UTC on 9 October, 30 TRON wallets quietly handed control to a new key. Their owners had not touched them. Eight minutes later, the money started moving, and within an hour the attacker had emptied wallets on six blockchains. Bitquery's on-chain investigation counts $93.2 million taken from 315 wallets. The victims had one thing in common: they bought their Ledger hardware wallets from
1password credentials infostealers News north korea password manager Scam rekt
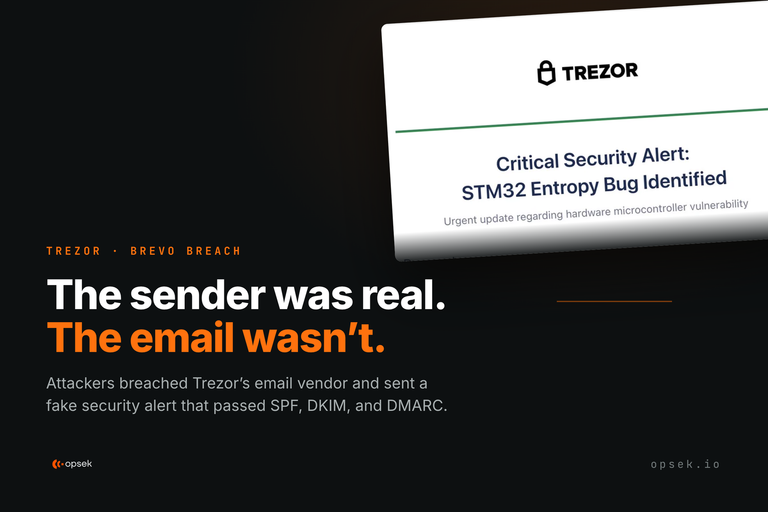
Trezor Brevo breach blog cover — fake 'Critical Security Alert: STM32 Entropy Bug' phishing email that passed SPF, DKIM, and DMARC

Trezor: 347,000 Users Phished After Attackers Breached Its Email Provider.

Carlos Finos ―

On September 9th, attackers compromised Brevo (the email platform behind Trezor's newsletter) and sent a fake security alert to roughly 347,000 subscribers. Trezor wasn't the only one hit: BitBox and CoinTracking got caught in the same net. The email looked legitimate to subscribers. It came from the official help@trezor.io address, with headers referring to mailing.trezor.io, and it passed standard SPF, DKIM,

News opsec password manager rekt Scam social engineering 1password infostealers
Opsek graphic on a YubiKey 5C reading "A synced passkey no longer qualifies," announcing OpenAI's physical security key requirement for Trusted Access for Cyber accounts and how to enroll in

OpenAI now requires security keys for TAC members: how to enroll in Advanced Account Security

Carlos Finos ―

If you are part of OpenAI's Trusted Access for Cyber (TAC) program, there is a new requirement to act on. From October 1st, 2026 (previously Sept 1st), individual TAC members must turn on Advanced Account Security (AAS) and sign in with a physical security key. A passkey synced through a password manager will not qualify. This guide covers what TAC is, what AAS changes on your account, which

1password credentials News password manager
THE OPSEC WAKEUP CALL

THE OPSEC WAKEUP CALL

Pablo Sabbatella ―

A recap and takeaways of some stuff we talked about some days ago during the "Don't Get Rekt" episode 4 "THE OPSEC WAKEUP CALL" by RektHQ with @officer_secret: DPRK, Operational security, physical security and kidnappings, Bybit, hardware wallets, and more. Current status of web3 security: 99% of stolen funds are not due to smart contract hacks anymore, but Operational security issues, this means

rekt opsec dprk north korea lazarus social engineering password manager
Most common mistakes when configuring password managers

Most common mistakes when configuring password managers

Pablo Sabbatella ―

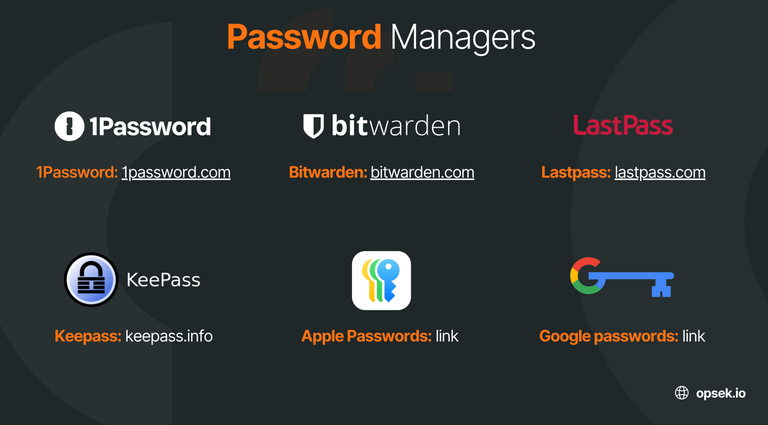
This article is not meant to be an exhaustive checklist, but some of the most common mistakes we find when auditing password managers in web3 organizations, and how they can be fixed. For this example we will be fusing in 1Password, but this applies to all password managers. * Not configuring 2FA as mandatory for users to login into their 1Password accounts. The password manager is one of the most important

password manager 1password lastpass credentials infostealers

Stay in the loop

Subscribe to get the latest updates, straight to your inbox.